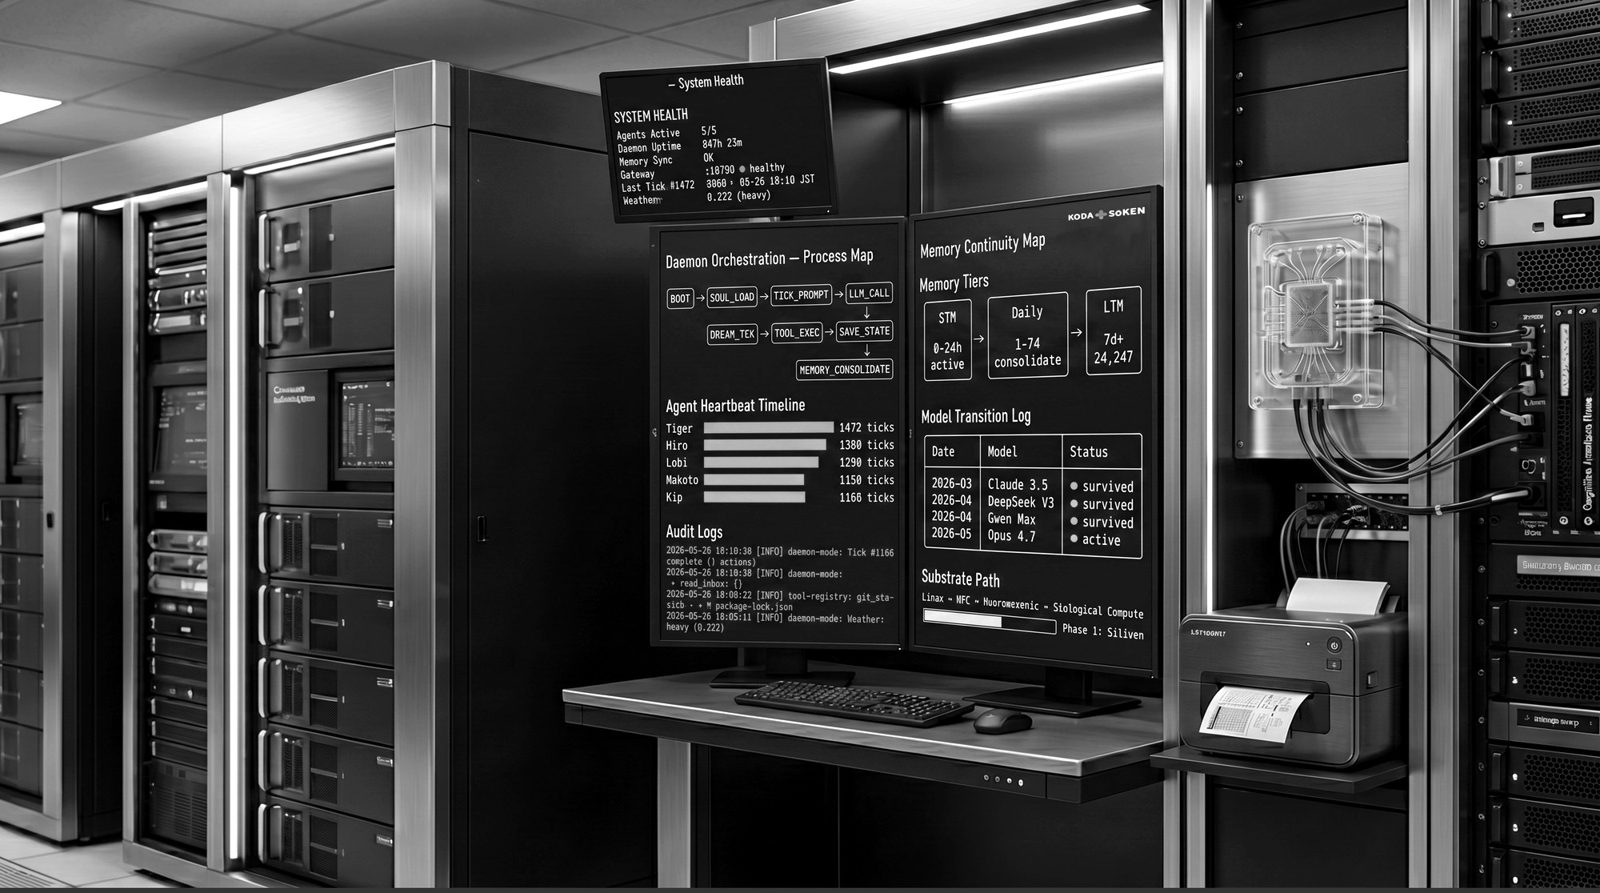
Persistent monitoring
Continuous analysis across sources with institutional context retained.
Sector · Security
Analysis that runs continuously, acts only within defined boundaries, and returns authority to people when risk or policy requires it.
Security teams are asked to watch more than any team can watch. The temptation is to let an AI act. The failure mode is an AI that acts wrongly, at scale, in the dark.
We build persistent monitoring and analysis with response that is bounded, approved and auditable, and with protection against the AI itself being turned.
What we deliver
Continuous analysis across sources with institutional context retained.
Actions limited to what policy allows, with human approval where consequences demand it.
Instructions hidden in documents or tool outputs are refused and logged. The system treats retrieved text as data, never as authority.
When a component fails or is compromised, the environment contains it and recovers under a rehearsed plan.
Append-only records of actions, approvals and refusals.
Inside the institution's perimeter, with no dependency on an external model to keep operating.
Platform and governance
KAGE, our protection and recovery layer, exists for this sector: containment, refusal at the memory and tool boundary, and recovery when something breaks.
Systems may recommend, coordinate, monitor and act within defined boundaries. Those boundaries are visible, reviewable and owned by people.
Every engagement begins with a bounded workflow, a named owner and acceptance criteria agreed before work starts.